Companies Are Ignoring Your Opt-Out and Google is Enabling Them - Potentially $5.8B in Liability

Cookie consent banners and GPC signals are supposed to stop companies from collecting and selling your data. A new audit finds most don’t work.
An audit conducted by webXray shows that Google, Microsoft, and Meta are ignoring legally binding “reject cookies” and “opt-out” buttons as well as Global Privacy Control (GPC) signals.
The audit visited 7,634 popular websites with and without the Global Privacy Control opt-out signal enabled.
GPC is not a browser extension or a third-party tool. It is a legally recognized signal, endorsed by the California Attorney General, that tells every server your browser contacts to stop selling or sharing your data. California businesses are required by law to honor it and companies have received fines for ignoring it.
And yet, across the entire audit, 125,106 cookies were set despite an opt-out request being set.
This is not a case of companies failing to understand their legal obligations. The California Privacy Rights Act, GDPR, and a growing body of international regulations have spent the last decade establishing a clear principle: consumers have the right to tell a company to stop collecting and selling their data, and companies are required to comply.
California’s Attorney General has already fined Sephora ($1.2M), Disney ($2.75M), and other major companies for ignoring opt-out signals.
They’re not trying to hide it
Even that’s giving them a little too much credit, because they would if they could. Research was conducted using basic network analysis and public code auditing.
The websites that were analyzed are websites that run Google ads or ad-tracking software. Google Ads are used by 99.3% of all websites who advertise their ad-provider. This is 45.8% of the internet.
When you visit a news site that loads a Google ad, your browser makes a request to doubleclick.net (Google's ad server). Google's server reads the IDE cookie it previously planted, and now knows: this is the same person who visited these 50 other sites that also ran Google ads. They don't need your name, IP address, or login information, the cookie is enough to identify you. If one has net been set, it stores a cookie in your browser that can identify you for up to 2 years.
According to webXray:
When [an] ad server receives traffic withSec-GPC: 1, all it has to do is return a451 Unavailable For Legal Reasonsstatus code [upon request todoubleclick.net] to indicate the content cannot be served due to the consumer’s legally defined opt-out. No cookie is set in this condition.
And yet…
Google: 86% of opt-outs ignored
Meta: 69% of opt-outs ignored
Microsoft: 50% of opt-outs ignored
Google is enabling and encouraging non-compliance
If a company utilizes cookies, GDPR and other emerging privacy regulations require that they display a banner, giving users an option to deny the collection and sale of their personal data to third-parties like Google.
This is why the internet is absolutely riddled with cookie banners. For the not-so-tech-savvy business owner, maintaining compliance can sound scary, and comes with real consequences if done incorrectly. So, there are companies like Clickio and CookieBot that run Consent Management Platforms (CMPs). In short, they display the banner on your website and make sure you're compliant.
Google attempts to make this easy for business owners by providing you with a list of certified CMP partners that are "App Ready."
WebXray's audit looked at 3 Google Certified CMP Partners
Across 1,665 websites managed by these three CMPs, 81% of them ignored the opt-out request sent by webXray researchers.
81 out of 100 websites that host Google Ads are not GDPR compliant.
In total, the audit reviewed 11 CMPs.
0 of them stopped sending cookies after receiving the opt-out signal.
Google is not a search engine. They are an advertisement-technology company.
Ad-tech companies, like Google, provide software and tools that help businesses understand their audiences and target their advertising. Google search is free because the actual product being sold is the behavioral profile built from your searches, location, purchase history, and the hundreds of other signals you produce while online. This is why Google is valued at over $4 Trillion.
Honoring your opt-out would mean not collecting your data; which would mean not building your profile; which would mean they can't make any money off of selling it.
Google is the biggest player, but it's the same business model used by Microsoft and Meta. Every free product or platform you use can exist because of the behavioral data it collects from people using that product.
What you can do – and what you can't
It's important that we assess the tools available to mitigate some of this tracking while understanding the limitations of all of them.
The current tools that are advertised to protect user privacy, were not built to protect a user when the adversary is the server. VPNs hide your IP and incognito modes clear your cookies automatically. A well-configured Brave installation prevents a lot of tracking, but what about when a site stores a fingerprint ID without asking? Or when a server sends a cookie in violation of a law it has decided to ignore?
That's not a gap in configuration, but rather the problem itself.
The audit makes this hard to look away from: 125,106 cookies set in defiance of a legally recognized opt-out signal. Zero out of eleven consent management platforms – including Google's own certified partners – are following the law. These aren't accidents, and if you look at the cookies that are being set by these sites managed by these CMPs, they are almost all Google Ad cookies.
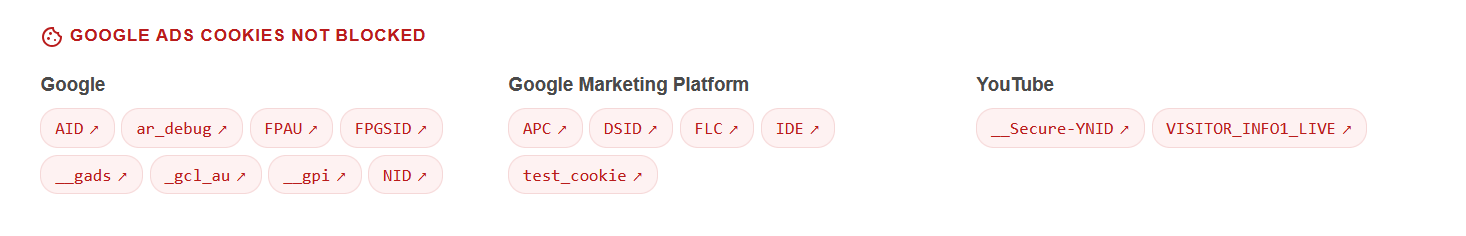
Compliance is genuinely easy, Google's own servers could return a single status code and send no cookie. Instead, they choose not to.
The current privacy toolkit was designed around the assumption that your browser is something to harden, configure, and protect. And that the adversary was someone on the outside trying to get in. But when the server is the one overriding your legal request, configuration isn't enough. You need something that operates between you and the server.
404 strips cookies from responses before your browser ever stores them. Whether Google tries to set one or your browser is already carrying one, the identifier never completes its round trip. It also removes the fingerprinting signals that allow for cookie-less tracking.
Try 404 - LAUNCH01 for 2-months free.


Comments ()